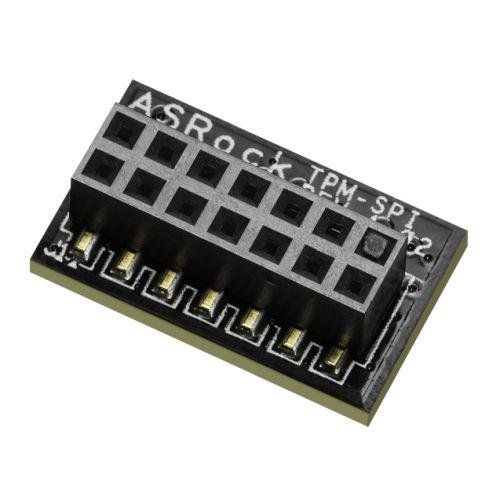
Asrock (TPM-SPI) TPM Module, 14-1 TPM Header, SPI Interface, Family 2.0, Level 00, Revision 01.16
ASRock
Compare today's prices on the "Asrock (TPM-SPI) TPM Module, 14-1 TPM Header, SPI Interface, Family 2.0, Level 00, Revisi...
Available From
Back to the Office
Quzo UK
Amazon
Ebay
Product Description
Compare today's prices on the "Asrock (TPM-SPI) TPM Module, 14-1 TPM Header, SPI Interface, Family 2.0, Level 00, Revision 01.16".
Asrock (TPM-SPI) TPM Module, 14-1 TPM Header, SPI Interface, Family 2.0, Level 00, Revision 01.16
Secure your system against modern threats with this dedicated TPM 2.0 module designed for motherboards equipped with a 14-1 pin SPI TPM header. By providing a hardware root of trust, it enables robust encryption of sensitive data, enhanced password protection, and strict platform integrity checks. This module is essential for businesses, remote workers, and privacy-conscious users who need to meet the security standards required by Windows 11, BitLocker drive encryption, and advanced enterprise features like Intel Trusted Execution Technology. With its plug-and-play SPI interface, installation is straightforward, and the module works seamlessly with compatible ASRock boards and other systems supporting the standard 14-1 pin layout.
- Compliant with TPM Main Specification Family 2.0, Level 00, Revision 01.16
- SPI (Serial Peripheral Interface) for reliable, low-latency communication
- Supports Intel TXT (Trusted Execution Technology) for hardware-level security
- Fully compatible with Microsoft Windows security features including BitLocker and TPM 2.0 requirements
- Works with Google Chromebooks for verified boot and firmware protection
- Standard 14-1 pin header for easy integration with compatible motherboards
- Delivers cryptographic key generation, secure storage, and remote attestation
Add this TPM module to your build to unlock essential security capabilities and ensure your system meets modern compliance standards.
GTIN: 4711430523651
Discover More From ASRock